News Made Clear · Loading…
Category
Regions
Continents
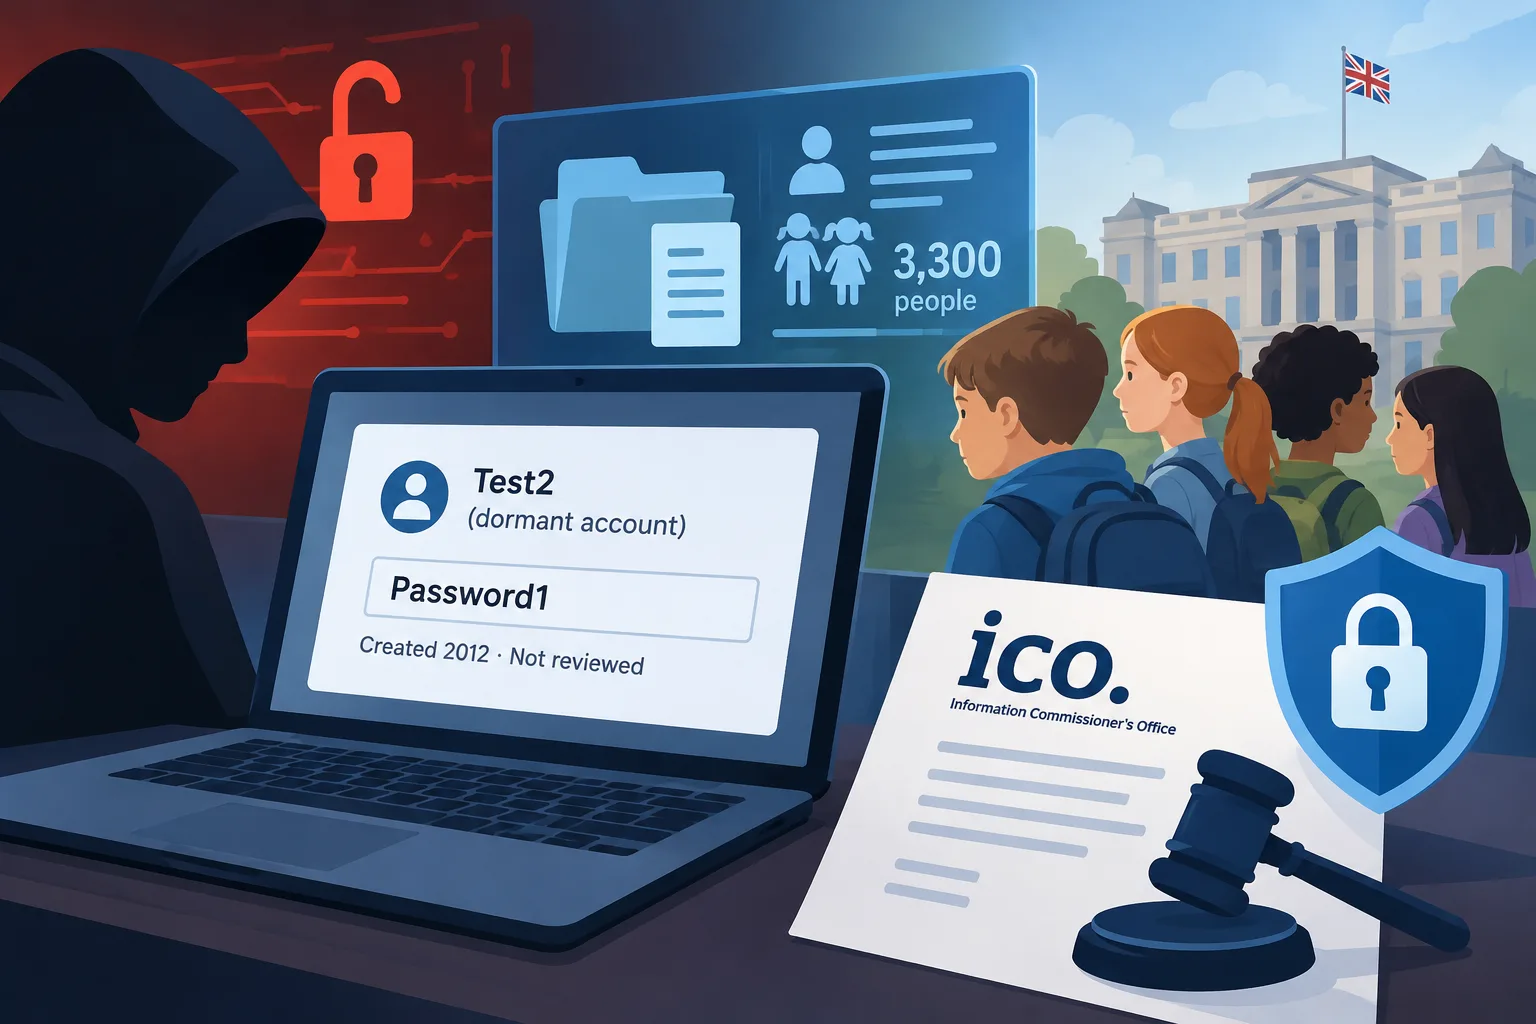
Weak password on dormant account exposed data of 3,300 people, watchdog says
Loading statistics…
A dormant account using the password “Password1” was exploited in a ransomware attack that exposed information belonging to 3,300 people, mostly children. The UK data watchdog has reprimanded the IT provider and the organisation whose systems were breached.
Review information is loading.
A dormant test account protected by the password “Password1” was used in a 2024 cyber-attack that exposed personal information belonging to 3,300 people, mostly children, the UK’s Information Commissioner’s Office (ICO) says. The watchdog has reprimanded IT provider Ogi Networks Limited (ONL) and Welsh public-sector organisation Data Cymru over the incident. [1]
The ransomware attack on 1 November 2024 encrypted 182.7GB of data and stole 42GB from Data Cymru’s systems. The exposed information related to two projects supporting children and families, according to the BBC’s report of the ICO’s findings.
The test account, called Test2, was created in 2012 and remained in place for more than 12 years without being audited or removed. The ICO said the password could be compromised in less than a second. It also found that administrator accounts on three affected systems had used the same password for that period.
The watchdog said both organisations breached UK GDPR requirements by failing to protect their systems properly and check regularly that security measures were effective. It said Data Cymru had not put a data-protection agreement in place with ONL, leaving a gap in responsibility between the organisations. It also faulted Data Cymru for failing to ensure the dormant account was identified and removed, or brought up to stronger password standards.
ONL said it accepted the ICO’s findings and had acted on them. A spokesperson said the account “should have been removed long before criminals were able to use it” and that the company brought in independent cyber-security specialists. The spokesperson said the breach was limited to the server ONL hosted for Data Cymru and did not affect information held for other customers.
Both organisations have since strengthened account controls and introduced periodic reviews, including multi-factor authentication. ONL said it worked with Data Cymru within a week of the attack to check accounts on its network and disable those no longer needed. The organisations signed a data-processing contract on 30 April 2025.
ICO investigations chief David Doodson said the failures did not rest with one organisation alone. The watchdog urged organisations to use strong passwords, protect remote access with multi-factor authentication, review accounts regularly and make clear who is responsible for cyber-security when services are outsourced.
How do we know?
1 listed sources · explore evidence, limitations and provenance.
Sign in to give this article a thumbs up or down.
About this discussion and AI questions
Private test discussion. Comments are readers’ views and are not yet automatically fact-checked. Editing is available for 60 seconds after posting.
Sign in with a confirmed reader account and choose a username to read comments and participate.
Sorting applies to top-level comments; replies remain oldest first. New comments and likes can change the order. Refresh for the current ranking.
Loading comments…